Galactic's Incident Response Seminar
Know exactly what to do when an incident hits.
A free, one-day virtual seminar that gives security teams, MSPs, and business leaders a tested response process before they need one.
November 11, 2026 · 10:00 AM ET · Full Day · Virtual · Free
The State of Incident Response in 2026
73% of organizations admit they wouldn't be fully ready if a significant cyberattack hit today, and 89% point to the same reason: limited executive and board involvement in IR readiness.
Attackers now hand off stolen access to a secondary threat group in 22 seconds, down from over eight hours in 2022. Your IR program should exist before that clock starts.
37%
Of organizations don't have a comprehensive incident response plan in place.
Source: TransUnion State of Incident Response Readiness 2026
42%
Of security professionals are confident in their team's ability to detect and respond to an attack.
Source: ISACA State of Cybersecurity 2026
22 secs
Median time from initial access to secondary threat group handoff, down from 8+ hours in 2022.
Source: Mandiant M-Trends 2026
$4.99M
Global average cost of a data breach, up 12% in a single year.
Source: IBM Cost of a Data Breach Report 2026
Build It Before You Need It
November 11 is when you and your team build the process, work through the hard decisions, and leave ready to execute.
You'll be able to:
- Stop improvising and start executing when the alert fires.
- Read an attack while it's moving and cut it off before it spreads.
- Make the hard calls, pay or don't, disclose now or later, having already worked through them.
- Demonstrate to everyone counting on you what a well-run response looks like from the inside.
The Sessions
Wednesday, November 11, 2026 · 10:00 AM – 4:55 PM ET (7:00 AM – 1:55 PM PT)
01 The 2026 Threat Landscape: What's Changed, and What It Means
Seth Loe, President and Chief Security Officer · 10:00 AM ET
The threat environment has changed enough in the past year that IR programs built on older assumptions are working with an incomplete picture. Seth opens the day by mapping what attackers are doing now, where they're getting in, and what that means for how the sessions that follow should be applied.
02 Anatomy of a Response: First Alert to Final Report
Aidan Brown, Security Analyst · 10:45 AM ET
Aidan covers the IR lifecycle from beginning to end, what each phase involves, and what separates a structured response from one that improvises under pressure. This session establishes the shared framework the rest of the day builds from.
03 Detection & Analysis: Reading an Incident in Motion
Aidan Brown, Security Analyst · 11:40 AM ET
Detection without analysis is just noise. Aidan covers how to move from an initial alert to a clear picture of what happened and what the right next step is, with a focus on making sound decisions when information is still incomplete.
04 Eradication & Recovery: Removing the Threat and Restoring Operations Safely
Cody Kretsinger, Director of Security Research · 12:25 PM ET
Getting back online is only part of the job. Cody covers how to eradicate a threat thoroughly before recovery begins, what clean means in practice, and how to validate it so operations restore without reopening the same exposure that started the incident.
05 Leading Through an Incident: Decisions, Disclosure, and the Message
Max Kurek, VP of Marketing · 2:15 PM ET
Incident response has a business and communication dimension that runs parallel to the technical one. Max covers how to make the case for preparedness, what stakeholder communication looks like during an active incident, and how leadership decisions shape outcomes before the first alert fires.
06 Inside the Quarantine: Working a Compromised Machine Live
Collin Page, CISSP, Security Advisor · 3:00 PM ET
Collin walks through a practical application of the IR lifecycle on an infected machine quarantined from a network by an EDR solution, covering the real decisions and competing priorities that come up when the framework meets an actual incident.
07 Playbooks & Tabletops: Break Your Plan Before an Attacker Does
Cody Kretsinger, Director of Security Research · 3:55 PM ET
Cody covers how to build playbooks that hold up under real conditions and how tabletop exercises surface the gaps before an actual incident does.
08 Wrap-Up and Q&A
Full Panel · 4:40 PM ET
The full session roster comes together to close the day with open Q&A and a clear path for applying the IR framework to your own environment and client relationships.
The Presenters
Seth Loe, CISSP
President and Chief Security Officer
Seth Loe has prepared hundreds of organizations to respond to cyber incidents. Before Galactic, he was CIO of a nationwide healthcare provider and ran security operations for an MSP. He teaches from real incidents, with a focus on what it takes to stick to the plan when everything is going sideways.
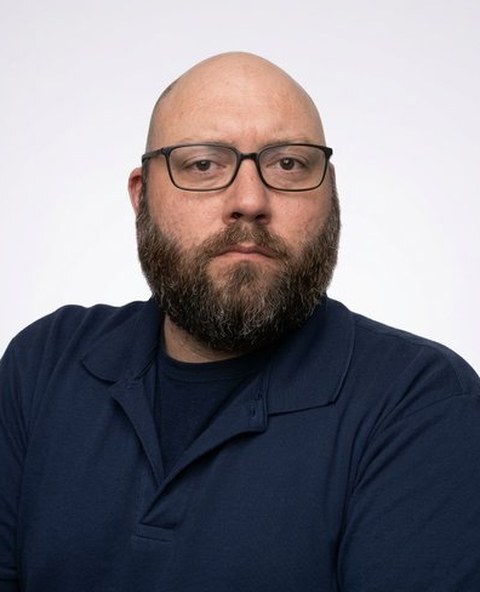
Cody Kretsinger
Director of Security Research
Cody Kretsinger made worldwide headlines as a hacker. Now he helps organizations stay out of them. He has worked both sides: penetration testing and red teaming on offense, SOC leadership and incident response on defense, including building a 24/7 SOC for an MSSP. At Galactic, he leads security research into how attackers operate so defenders can get there first.
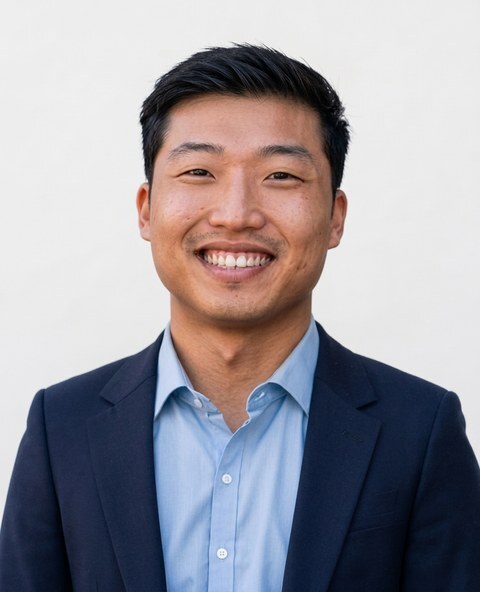
Aidan Brown
Security Analyst
Aidan Brown tracks the threats that matter and turns them into guidance that engineers and executives can both act on. His work spans threat intelligence, security research, and security awareness, and it starts from hands-on analysis.
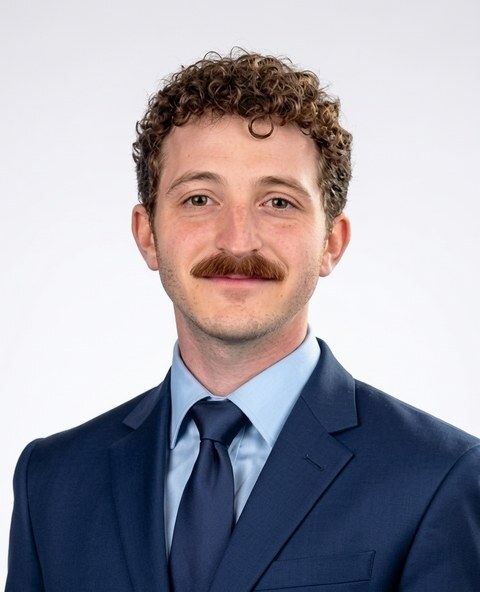
Collin Page, CISSP
Security Advisor
Collin Page has spent more than ten years in cybersecurity, much of it in healthcare and finance. He turns penetration test findings into a plain-English list of what to fix first and what to have ready if one of those gaps gets used against you.
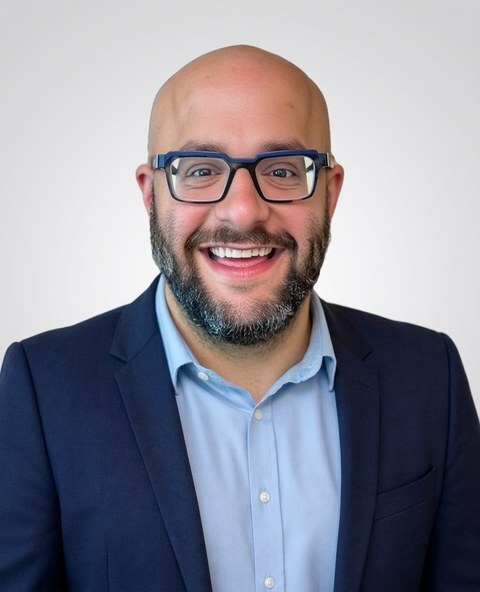
Max Kurek
VP of Marketing
Max Kurek spent 5 years leading executive security engagements as a vCSO. Now Galactic's VP of Marketing, he's worked for years communicating security programs to business audiences by translating risk to business impact. In an incident, that skill becomes the job: deciding what to say, to whom, and when. He covers the communication and leadership calls that decide how an organization comes out the other side.
The Resources
Every attendee walks away with a package of resources built to put what they learned into practice immediately.
The Galactic IR Playbook Binder
A comprehensive library of step-by-step incident response playbooks covering 49 different scenarios, with detailed instructions on how to use them.
The IR Playbook Skill
An AI skill built around the playbook library that you can load directly into your AI model of choice and put to work immediately.
Tabletop Scenarios
A set of ready-to-run tabletop exercises you can take back to your team and run against your own environment.
Who This Is For
This seminar is built for security and IT leaders who own the response plan, MSP and MSSP teams who run incidents for their clients, and executives and business owners who make the decisions when systems go dark.
If an incident lands on your desk, or the decision lands on your name, this day is for you.
Register today and walk into the incident prepared.
One day, free, with the people who've done this before.